Quick answer
The 2023 MGM Resorts hack reportedly began when attackers phoned the IT help desk posing as an employee. Ransomware then disrupted casinos and bookings, costing about $100 million in one quarter. Scattered Spider is blamed, but no court has tied a named person to MGM. Stronger caller checks and phishing-resistant MFA are the key fixes.
Key takeaways
- • The MGM Resorts hack reportedly started with a social engineering call to the IT help desk, a claim that was never independently confirmed.
- • MGM estimated about $100 million in impact for the quarter and less than $10 million in one-time costs.
- • Customer names, birth dates and license numbers were taken; MGM says no card or bank data was.
- • Scattered Spider and ALPHV are blamed, but public court cases so far do not name MGM.
- • Call-back checks, second approvers and FIDO2 keys are the strongest help desk defenses.
Table of contents 17 sections
- What Happened in the MGM Resorts Hack?
- MGM Cyber Attack Timeline
- How Did One Phone Call Lead to Ransomware?
- What Went Wrong? Six Weak Points the Attack Exposed
- 1. Identity Checks a Stranger Could Pass
- 2. Resets Granted Over the Phone
- 3. MFA That Could Be Talked Around
- 4. Too Short a Path to the Crown Jewels
- 5. Shared Risk With Outsourced Support
- 6. Old Customer Data Still on File
- The Cost in Money and Data
- Who Was Blamed, and How Strong Is the Evidence?
- What Happened After the Attack?
- What Does This Mean for Organizations in Pakistan?
- Seven Defensive Lessons From the MGM Resorts Hack
- Rehearsing Help Desk Attacks in PSTA's Security Labs
- Ask Your Help Desk One Question Tomorrow
On 11 September 2023, guests at MGM Resorts properties in Las Vegas found slot machines dark, card terminals down and the booking website offline. The MGM Resorts hack had started, and the company later estimated a hit of about $100 million to one of its September earnings measures. The part that matters most for you is how ordinary the first step reportedly was: a phone call to an IT help desk.
This case study treats the MGM Resorts hack as a set of weak points rather than a thriller. Here is what you will get:
- How a reported 10-minute help desk call could open the door to a casino network
- Six weak points the attack exposed, and why each one is common in Pakistan too
- The confirmed cost, the stolen customer data and the $45 million settlement
- Who was blamed, and why no public court record has yet tied a named person to MGM
- Seven help desk defenses you can apply in a bank, telco, hospital or call center
What Happened in the MGM Resorts Hack?
According to BleepingComputer's report on the incident, the disruption hit MGM's website, its reservation system and systems on the casino floor, including slot machines, card terminals and ATMs. MGM told investors on 12 September that it had found a "cybersecurity issue" affecting some of its US systems.
Within days, the ransomware group ALPHV (also called BlackCat) took credit. Security reporting linked the hands-on work to an ALPHV affiliate known as Scattered Spider. The group claimed the attackers encrypted more than 100 ESXi hypervisors, the servers that run many virtual machines at once. The Register reported that claim but warned readers to treat it with caution, since it came from the criminals themselves.
Caesars Entertainment, another Las Vegas operator, was hit in the same weeks. Its filing blamed social engineering against an outsourced IT support vendor. That detail helps explain the wider pattern: the attackers went after people who reset passwords, not after software bugs.
MGM Cyber Attack Timeline
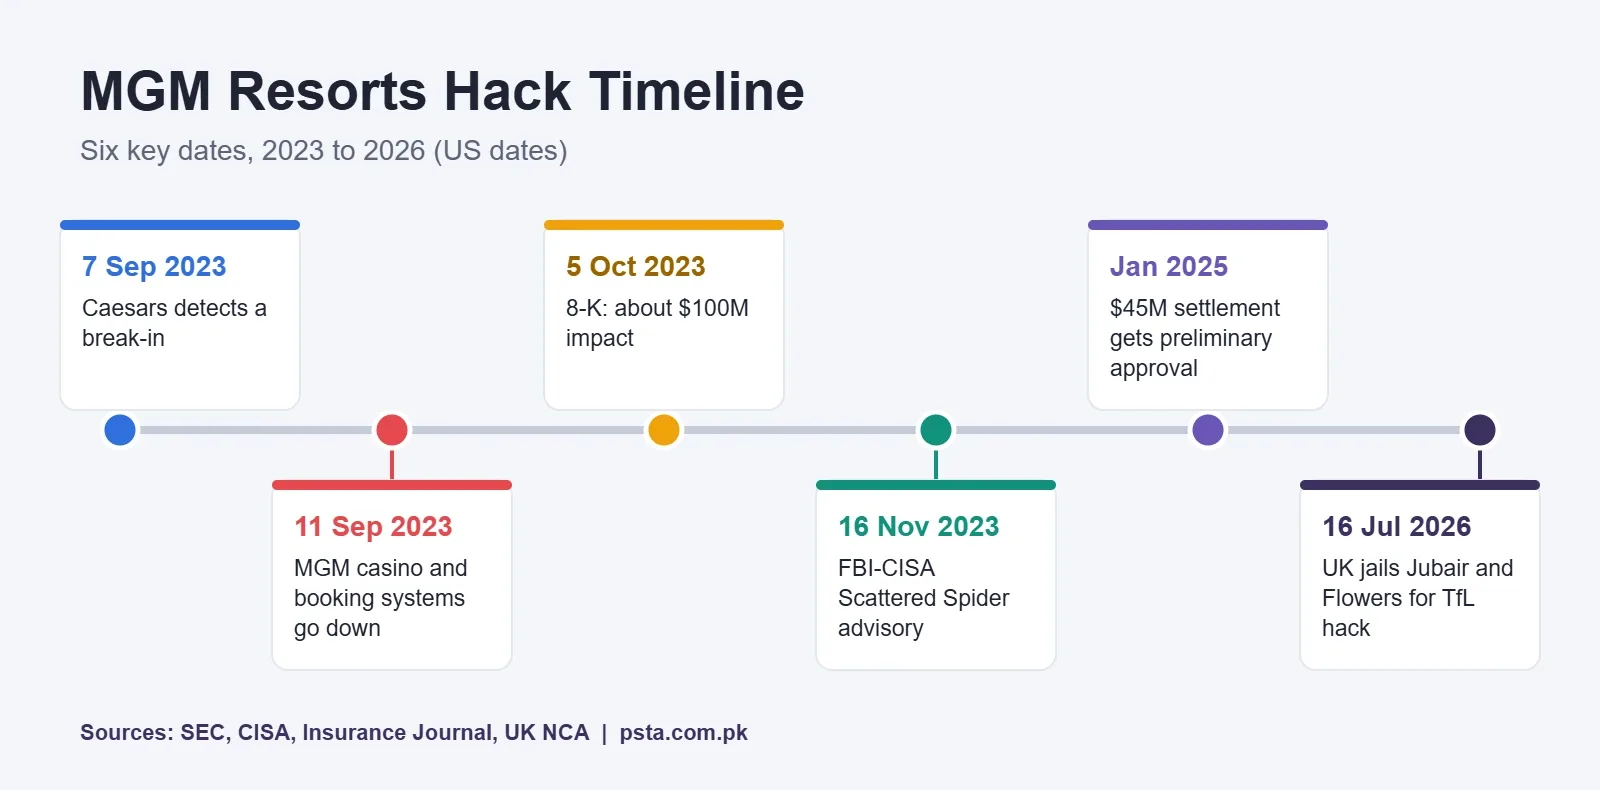
Las Vegas is 12 hours behind Pakistan in September, so a morning outage on the Strip landed in the evening for anyone watching from Lahore or Karachi. Dates below are US dates.
| Date | Event | Status of the fact |
|---|---|---|
| 7 Sep 2023 | Caesars detects a break-in linked to social engineering of an IT support vendor | Confirmed in Caesars' SEC filing, per The Register |
| 8 Sep 2023 | ALPHV says it first got into MGM's network | Attacker claim, not independently confirmed |
| 11 Sep 2023 | Slot machines, booking systems and the website go down; ransomware reportedly runs on ESXi servers | Outage confirmed; ESXi count is an attacker claim |
| 12 Sep 2023 | MGM issues a statement about a cybersecurity issue; ALPHV's "10-minute call" claim spreads online | Statement confirmed; call details unconfirmed |
| 5 Oct 2023 | MGM files an 8-K estimating about $100 million in impact and listing stolen data types | Confirmed (SEC filing) |
| 16 Nov 2023 | FBI and CISA publish a joint advisory on Scattered Spider tactics | Confirmed (government advisory) |
| Jan 2025 | Judge gives preliminary approval to a $45 million class settlement | Confirmed (court filing, per Insurance Journal) |
| 18 Sep 2025 | US unseals charges against Thalha Jubair for about 120 intrusions; MGM not named | Confirmed (DOJ) |
| 16 Jul 2026 | Jubair and Owen Flowers each get five years and six months in the UK for the Transport for London hack | Confirmed (UK National Crime Agency) |
How Did One Phone Call Lead to Ransomware?
On 12 September 2023, the malware archive account vx-underground relayed a post from ALPHV. As Engadget reported, the group said it found an MGM employee on LinkedIn, phoned the help desk while posing as that person, and gained access in about 10 minutes. Engadget noted that security researchers had not confirmed the story.
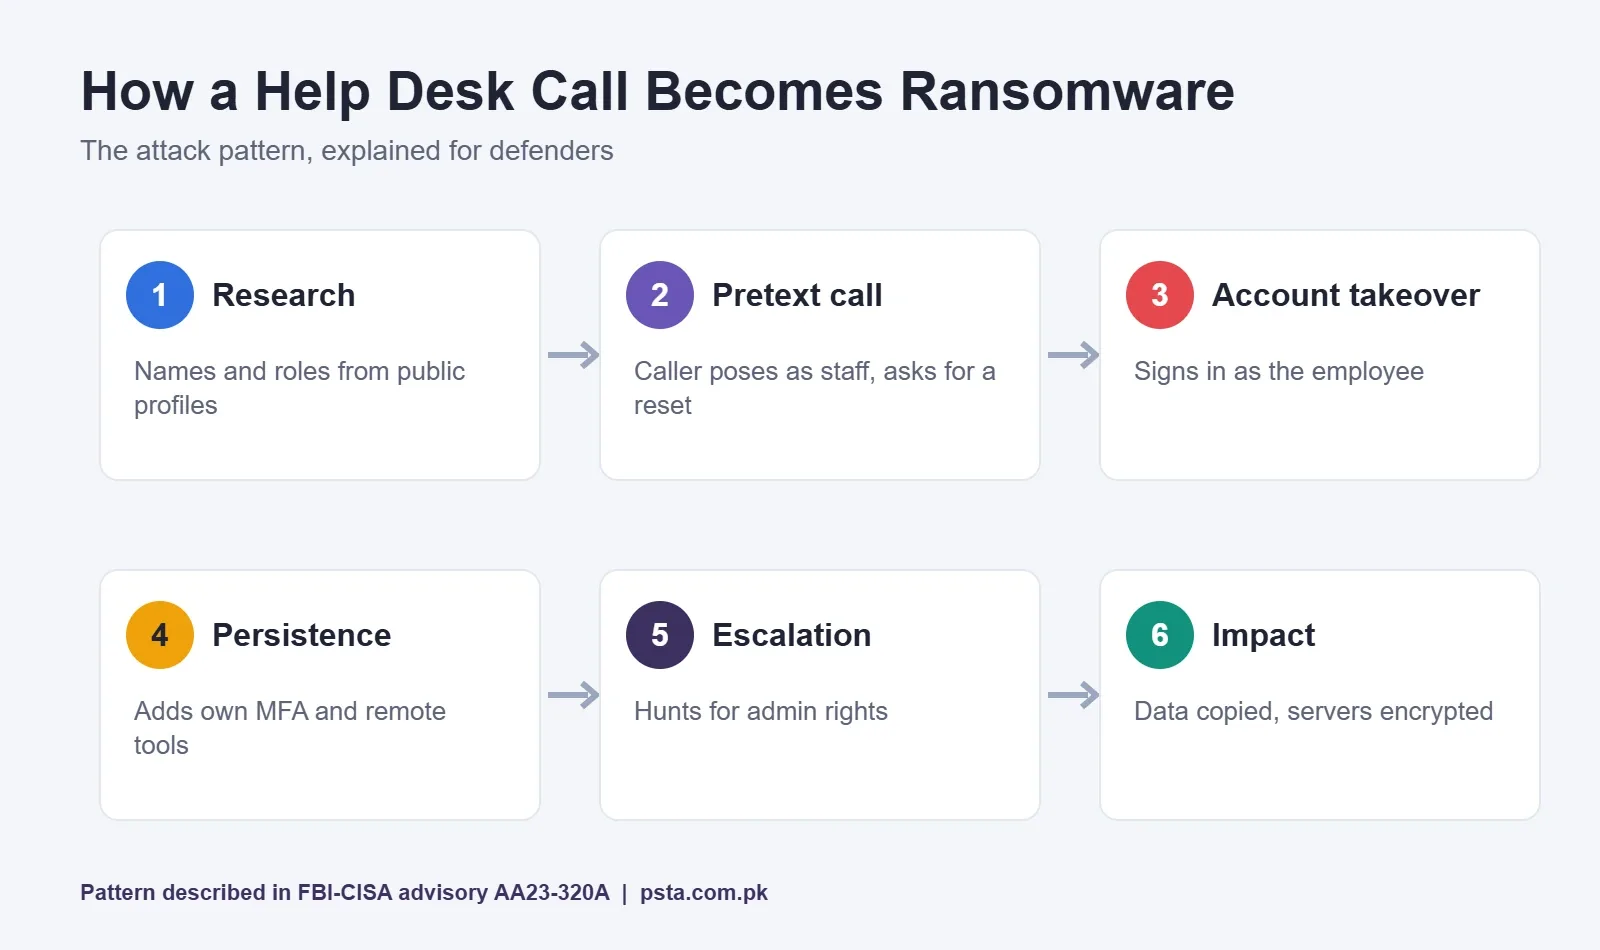
Treat the exact script of the MGM Resorts hack as unproven. The overall pattern, though, matches what the FBI and CISA later described in their joint Scattered Spider advisory (AA23-320A). At a conceptual level, the chain looks like this:
- Research: the attacker learns names, job titles and team structure from public profiles.
- Pretext call: the attacker phones the help desk as a staff member and asks for a password or MFA reset. A phone-based con like this is called a vishing attack.
- Account takeover: with the reset done, the attacker signs in as the employee, often through single sign-on.
- Persistence: the advisory describes attackers adding their own MFA devices and installing legitimate remote access tools so they can return.
- Escalation: they hunt for admin rights and the systems that run everything else, such as virtualization servers.
- Impact: data is copied out, then ransomware encrypts servers to force a payment.
Notice that no step needs a clever exploit. Each one abuses a normal business process. That is why help desk social engineering is so hard to stop with technology alone.
What Went Wrong? Six Weak Points the Attack Exposed
MGM has not published a full post-mortem, so nobody outside the company knows every internal detail. The weak points below come from the public record: MGM's filing, the attackers' claims, the Caesars disclosure and the government advisory. Read them as lessons, not as a verdict on MGM's staff.
1. Identity Checks a Stranger Could Pass
If ALPHV's account is close to true, the caller knew enough public detail to sound real. Questions such as employee ID, date of birth or manager's name are easy to collect. A check based on facts that are written down somewhere is not a strong check.
2. Resets Granted Over the Phone
The advisory describes attackers persuading help desk staff to reset passwords and MFA. When one phone call can hand over a working account, the help desk becomes the front door.
3. MFA That Could Be Talked Around
Push prompts, SMS codes and reset requests can all be defeated by a convincing person. CISA's advisory recommends phishing-resistant MFA based on FIDO or PKI, which it says resists push bombing and SIM swaps.
4. Too Short a Path to the Crown Jewels
Encrypting large numbers of hypervisors, as claimed, needs very high privileges. When a single stolen identity can reach the systems that run the whole estate, recovery takes much longer.
5. Shared Risk With Outsourced Support
Caesars pointed to its outsourced IT support vendor. Many companies hand password resets to a third party but never test that partner's caller checks.
6. Old Customer Data Still on File
MGM said the stolen data belonged to customers who did business with it before March 2019. Records kept for years after they are needed add risk without adding value.
The Cost in Money and Data
The most reliable source on the cost of the MGM Resorts hack is the company's 8-K filing of 5 October 2023. Here are the key figures from it and from the later lawsuit.
| Item | What the record shows |
|---|---|
| Hit to earnings | About $100 million to Adjusted Property EBITDAR, mostly in Las Vegas, in the third quarter of 2023 |
| One-time costs | Under $10 million for consultants, legal fees and advisors in the same quarter |
| Hotel occupancy | 88% in September 2023, compared with 93% a year earlier |
| Data taken | Names, contact details, gender, dates of birth and driver's license numbers; Social Security and passport numbers for a limited number of people |
| Data MGM says was not taken | Passwords, bank account numbers and payment card data |
| Insurance | MGM said it expected its cyber insurance to cover the operational impact |
| Lawsuit | $45 million class settlement covering the 2019 and 2023 breaches |
The filing did not mention any ransom payment. For the MGM data breach settlement, Insurance Journal reported that a federal judge in Nevada granted preliminary approval in January 2025. Eligible people could claim $75 if a Social Security or military ID number was exposed, $50 for a passport or driver's license, and up to $15,000 for documented losses.
Who Was Blamed, and How Strong Is the Evidence?
Be careful to separate three layers of blame in the MGM Resorts hack.
Claimed by the attackers: ALPHV publicly took credit, and reporters identified the hands-on attackers as its Scattered Spider affiliate. Claims from criminals help investigators, but they are not proof.
Described by government: the FBI and CISA advisory of November 2023 says Scattered Spider targets large companies and their IT help desks, and has used ALPHV ransomware according to trusted third parties. The advisory text does not name MGM.
Tested in court: on 18 September 2025, the US Department of Justice announced charges against Thalha Jubair, then 19, of London. Prosecutors allege about 120 intrusions, including at least 47 US victims, and more than $115 million in ransom paid. These are allegations, and MGM is not named in the release. In the UK, the National Crime Agency says Jubair and Owen Flowers each received five years and six months on 16 July 2026 for the 2024 Transport for London intrusion. That release does not mention MGM either.
So the fair summary is this. Attribution to the Scattered Spider group is widely accepted and backed by the attackers' own claim. A court finding that a specific person carried out the MGM attack has not appeared in the public records reviewed for this article.
What Happened After the Attack?
MGM reported the cost to investors in October 2023 and said the impact on the fourth quarter would be minimal. Customers sued, and those cases were folded into the $45 million settlement alongside an older 2019 breach.
Caesars faced a parallel incident. Bloomberg reported that Caesars paid tens of millions of dollars, while the Las Vegas blog Vital Vegas reported $15 million against a $30 million demand. The Register, which relayed both reports, could not confirm either figure, and Caesars declined to comment.
The bigger change was in how defenders talk about help desks. The FBI and CISA advisory turned the Las Vegas story into a checklist: phishing-resistant MFA, allowlists for remote access tools, offline and immutable backups, and network segmentation. Law enforcement in the US and UK has since charged or jailed several people tied to the wider group, even if not for MGM itself. If you followed our Change Healthcare hack case study, you will recognize the ALPHV name from that 2024 attack too.
What Does This Mean for Organizations in Pakistan?
You do not need a casino to face the risk behind the MGM Resorts hack. Every bank, mobile operator, hospital, university and software house in Pakistan has someone who resets passwords. Many local call centers and IT firms also run help desks for foreign clients. A vishing call to Karachi or Islamabad can be the first step against a company abroad.
The same tricks already reach ordinary people here. Fake "bank officer" calls and requests for a six-digit code follow the same script, as our guide to fraud calls in Pakistan explains. The account takeovers in WhatsApp hacking cases usually begin with someone sharing a code they should have kept.
For businesses, the takeaway is simple. Your strongest firewall does little if a polite caller can get an admin password reset. Treat the help desk as a security control with written rules. Give staff the backing to say "I will call you back."
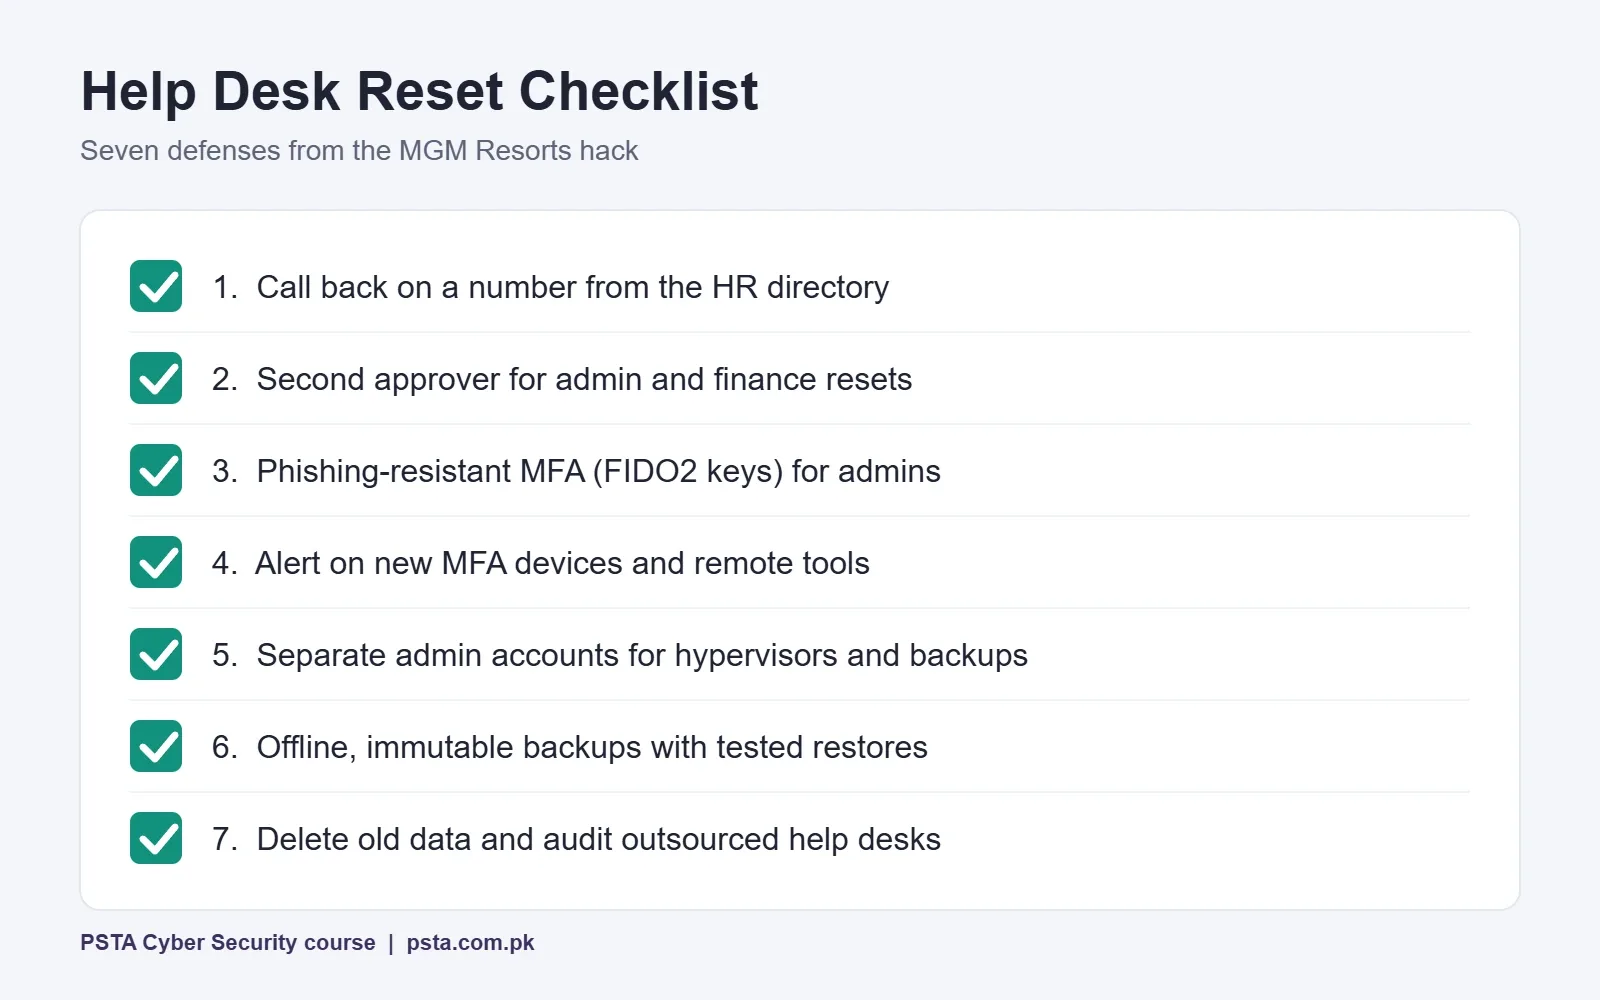
Seven Defensive Lessons From the MGM Resorts Hack
- Verify callers out of band. End the call and ring the person back on a number from your HR directory, not one the caller gives.
- Add a second approver for sensitive resets. For admin or finance accounts, require a manager's confirmation or an in-person or video check.
- Move admins to phishing-resistant MFA. Hardware security keys based on FIDO2 cannot be read out over the phone. Our two-factor authentication guide explains the options.
- Alert on new MFA devices and remote tools. A new authenticator or an unknown remote access program on a laptop should trigger a review.
- Separate admin identities. Keep virtualization and backup consoles behind separate accounts and network segments.
- Keep offline, immutable backups. Test a full restore at least once a quarter so you know how long recovery really takes.
- Delete data you no longer need, and audit your vendors. Old records and untested outsourced help desks both widen the blast radius.
Run a short vishing drill with your own help desk, with management approval, and record how many calls were handled by the book. That single number tells you more than a policy document.
Rehearsing Help Desk Attacks in PSTA's Security Labs
Cases like the MGM Resorts hack are part of how we teach. PSTA's Cyber Security & Ethical Hacking course is a 12-week program for beginners, taught on campus in Abbottabad or in live online classes from anywhere in Pakistan. The labs include recognizing phishing and social engineering, configuring defenses such as firewalls and VPNs, and investigating an incident with a written timeline. Your final project is a written security report on a real-world style case.
Students who want to go further into authorized testing can continue with the Advanced Ethical Hacking and Penetration Testing course. If you are mapping out exams, our cyber security certifications guide compares the common first steps. For other cases in this series, start with the Binance hack explained and the 2020 Twitter hack, which also began with phone-based social engineering.
Ask Your Help Desk One Question Tomorrow
Walk over to whoever resets passwords at your workplace and ask: "If I phoned you as the CEO and said I was locked out, what would you check before helping?" If the answer is a name and a date of birth, you have found your first fix. Write down a call-back rule, agree on it with your manager, and share it with the team this week. If you want guided practice with these defenses, PSTA's admissions team can talk you through the next batch on WhatsApp.
Frequently asked questions
How did hackers get into MGM Resorts?
The ALPHV ransomware group claimed its attackers found an MGM employee on LinkedIn, called the IT help desk while posing as that person, and got access in about 10 minutes. Security researchers have not confirmed that account. The pattern matches the help desk impersonation tactics the FBI and CISA described in their November 2023 advisory on Scattered Spider.
Did MGM pay the ransom?
MGM's October 2023 filing with the US Securities and Exchange Commission does not mention any ransom payment, and the company did not publicly confirm one. Caesars, hit in the same weeks, was reported by Bloomberg to have paid tens of millions of dollars, but Caesars did not confirm that figure to reporters.
Was customer card data stolen in the MGM data breach?
MGM said it does not believe passwords, bank account numbers or payment card data were taken. The stolen records covered customers who did business with MGM before March 2019 and included names, contact details, gender, dates of birth and driver's license numbers. A limited number of people also had Social Security or passport numbers exposed.
Who is Scattered Spider?
Scattered Spider is the name the FBI and CISA use for a cybercriminal group that targets large companies and their IT help desks. Its methods include phone impersonation, SMS phishing, MFA fatigue and SIM swapping, and the agencies say it has used ALPHV ransomware. People linked to the group have been charged in the US and the UK.
Has anyone been convicted for the MGM cyber attack?
Not in any public court record reviewed for this article. Thalha Jubair faces US charges over about 120 intrusions, and he and Owen Flowers were jailed in the UK in July 2026 for the Transport for London hack. Neither the US Department of Justice release nor the UK National Crime Agency release names MGM.
What is a vishing attack?
Vishing is voice phishing: a scam carried out by phone instead of email. The caller pretends to be a colleague, bank officer or support agent and pushes you to reveal a password, read out a code or approve a reset. Calling the person back on a number you already trust is the simplest way to stop it.
Could a Pakistani company face the same kind of attack?
Yes. Any organization where staff can reset passwords or MFA over the phone has the same weak point, whether it is a bank, telco, hospital, university or call center serving foreign clients. Written call-back rules, a second approver for admin accounts and hardware security keys reduce the risk without large spending.
Sources & references
- MGM Resorts Form 8-K, 5 October 2023 sec.gov
- FBI and CISA advisory AA23-320A: Scattered Spider cisa.gov
- US DOJ: UK national charged in multiple cyber attacks justice.gov
- UK NCA: Two sentenced for hacking Transport for London nationalcrimeagency.gov.uk
- Insurance Journal: MGM Resorts to pay $45M to settle data breach lawsuit insurancejournal.com
- The Register: Caesars confirms data theft as MGM outage drags on theregister.com
- BleepingComputer: MGM Resorts ransomware attack led to $100 million loss bleepingcomputer.com
- Engadget: Hackers claim a 10-minute phone call shut down MGM engadget.com
Last reviewed & updated on by Umar Qureshi. Written by the PSTA team in Abbottabad, Pakistan.

Umar Qureshi
Cyber Security & Ethical Hacking Course in Abbottabad - PSTA
Turn this guide into a career: hands-on training with real projects, online across Pakistan or on-campus in Abbottabad · 12 Weeks.
Comments
No comments yet — ask a question or share your experience.